

About Trustless MPC (tMPC)
Next-generation MPC security without custodial risk
io.finnet extends MPC and TSS with a platform for Trustless Multi-Party Computation (tMPC).
io.vault lets you generate public/private key material and distribute it between N signers, each with an individual amount of signing power. When signing a transaction, the threshold must be reached by a number of approved signers with enough total signing power to complete the operation. The key cannot be used unless enough signing power is contributed to the signing ceremony.
This allows you to enforce cryptographically secured signature approval policies. Try it out with our interactive widget:
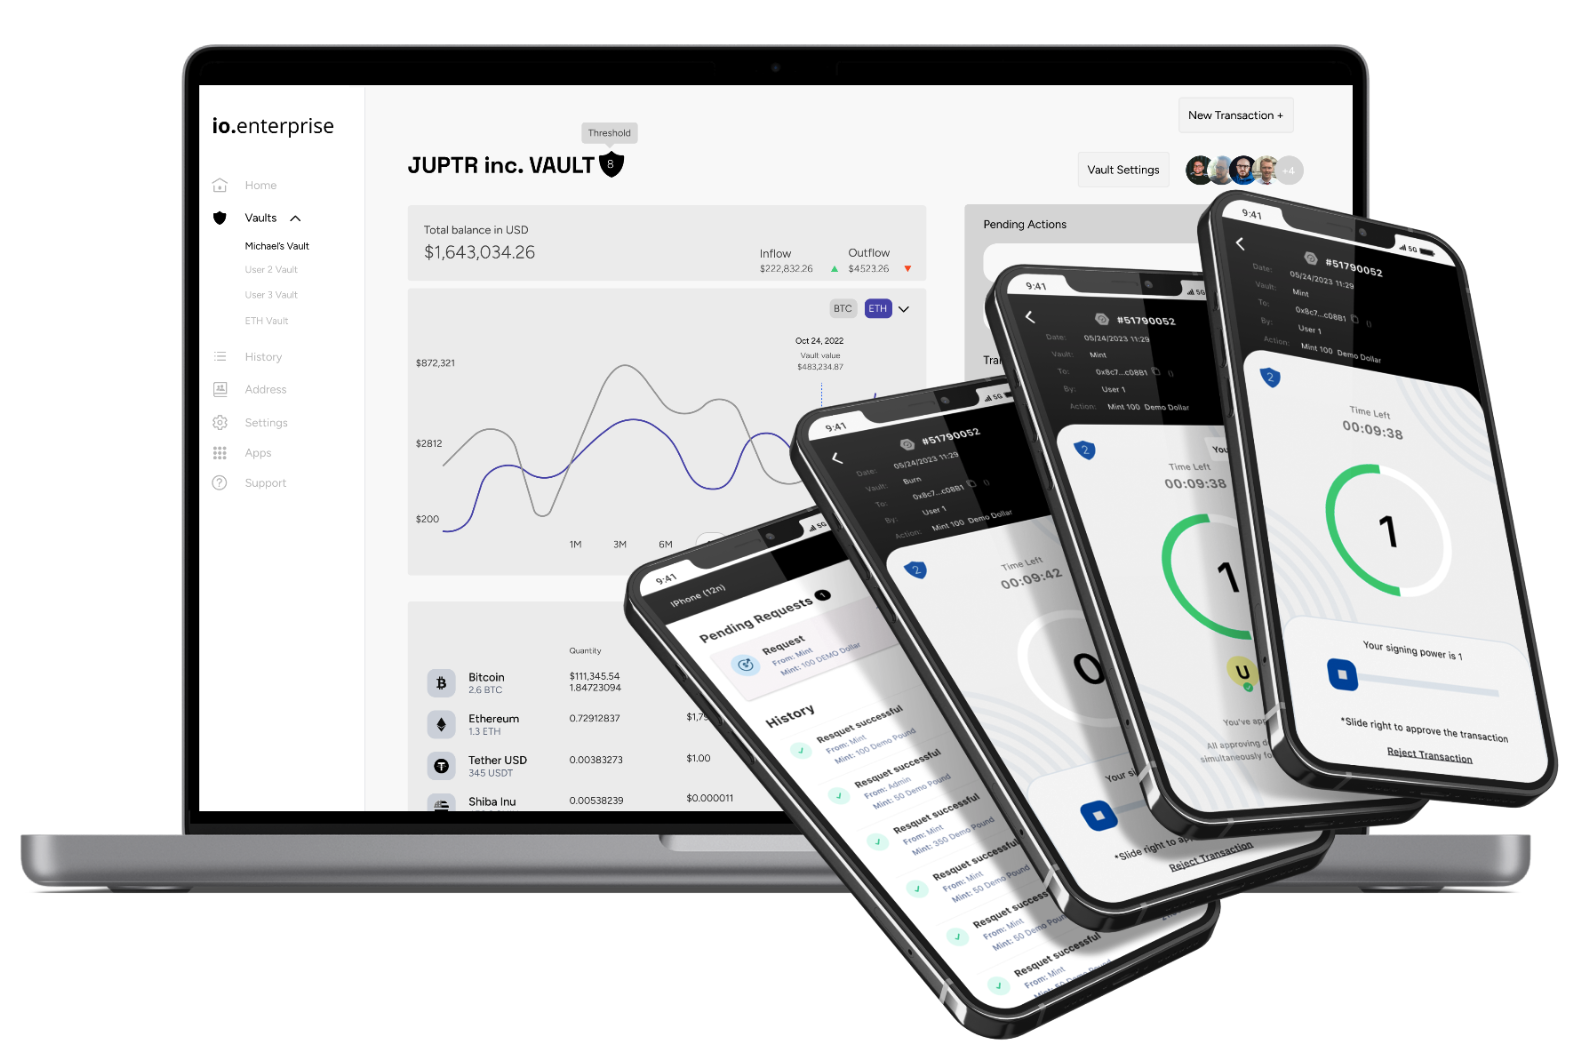
Threshold & Signers
Set the Vault Threshold
The amount of approvals required to sign a transaction or reshare request
Add Signers
Each signer added may participate in the approval and signing process for all transactions and changes made in this vault
With tMPC, key shares are generated and stored on signers' own devices, not on io.vault's servers. This eliminates reliance on io.finnet as a trusted party. Shares are never revealed to other signers or to io.finnet, and no full private key exists during normal operation.
tMPC is cross-platform and multi-device. As a distributed system built on a secure messaging layer, users can choose their own retail devices with full-resolution screens and proven secure enclave hardware, which eliminates blind signing and maximises flexibility. For automated workflows, you can use server-side policy management and signing with the Virtual Signer.
The tMPC stack supports weighted signing (signer power), server-based signing (Virtual Signer), a robust offline disaster recovery process, web3 dApp integration, and centralised exchange (CEX) connectivity.
In a disaster scenario where io.vault is unavailable, signers recover funds by pooling their key shares using an offline, open-source tool. The disaster recovery flow reconstructs the private key from a threshold number of signer backup files and their corresponding passphrases.
MPC, TSS, and tMPC work together to provide distributed trust and defence in depth for digital asset management.
Secure Multi-Party Computation (MPC)
MPC is a subfield of cryptography that enables multiple parties to jointly compute a function over their inputs while keeping those inputs private. In digital asset custody, MPC allows a private key to be split into shares distributed across multiple parties.
Key properties of MPC:
- Each party only has access to their own key share, not the full private key.
- Signing a transaction requires a threshold number of parties to contribute their shares.
- Even if some shares are compromised, the private key remains secure as long as the threshold is not met.
io.finnet uses MPC to generate key shares when you create a new vault. These shares are then distributed to the signers in the vault's signing party.
Threshold Signature Schemes (TSS)
TSS is a cryptographic protocol that allows a group to collectively sign a message or transaction, provided a threshold number of participants agree. Rather than using a single private key, TSS uses a configurable number of key shares to produce a valid signature for the corresponding public address. You can also set a threshold that determines how many shares are required.
This means you could have many key shares held in different locations, by different people. If one share is stolen, no assets are at risk because the attacker cannot reach the threshold alone.
Combined with MPC, TSS eliminates the single point of failure normally associated with self-custody of digital assets. It also lets you determine the security level for each vault (number of shares and required threshold) and distribute signing power across multiple people rather than relying on one trusted individual.
In a TSS setup:
- A private key is split into N shares, held by N parties.
- Any M out of N parties can collaborate to produce a valid signature (M <= N).
- The private key is never reconstructed in full.
When a transaction is initiated from io.vault, the TSS protocol works as follows:
- The transaction is distributed to all signers in the vault's signing party.
- Each signer uses their key share to partially sign the transaction.
- Once enough signers (meeting the threshold) have participated, the partial signatures are combined into a valid final signature.
- The signed transaction is broadcast to the blockchain network.
TSS ensures that no single party can unilaterally sign transactions, and compromising a subset of signers does not compromise the system. You can customise the threshold per vault based on your desired balance of security and availability.
Updated about 2 months ago